Tutorial for secure emailing with personal domain,Cloudflare, virtualmin and postfix
-
@phenomlab said in Tutorial for secure emailing with personal domain,Cloudflare, virtualmin and postfix:
By default, Virtualmin based domains have email which is accessible at https://yourserver.com:20000
hmmm acess seem to work, I log with root but Inbox doesn’t seem to load correctly.

After a moment I have this message :

If I log with my root account like always, I have this :

EDIT: seems Ok with other account. Seems root account doesn’t have inbox
@phenomlab said in Tutorial for secure emailing with personal domain,Cloudflare, virtualmin and postfix:
The MX record root.phenomlab.com is my VPS server
what is root.phenomlab.com on your virtualmin? it’s not a virtual server, jsut your hostname i guess
For example, I am login to virtualmin on adm.xxxx.fr (hostname of my server) so my mx field should be adm.xxxx.fr and not root.xxxx.fr right?
for dmarc and dkim, i’am not see for the moment, i see later
— EDIT:
my Dmarc configuration


@DownPW said in Tutorial for secure emailing with personal domain,Cloudflare, virtualmin and postfix:
For example, I am login to virtualmin on adm.xxxx.fr (hostname of my server) so my mx field should be adm.xxxx.fr and not root.xxxx.fr right?
Yes, correct.
@DownPW said in Tutorial for secure emailing with personal domain,Cloudflare, virtualmin and postfix:
For DKIM, I don’t quite understand. Once generated in the tools you gave, I understand for the DNS entry in CF but what do I do with the private and public key?
The private and public key can simply be stored. You do not have to do anything with these.
-
Seems port 25 OK

@DownPW said in Tutorial for secure emailing with personal domain,Cloudflare, virtualmin and postfix:
Seems port 25 OK
Not sure about that - see below from your server. When sending a
telnetrequest on port 25, there is no response. This typically means the port is closed on your side.
What SHOULD happen is this

However, it DOES respond on port 587

From recollection, your VPS is being hosted by Hetzner. Although you have no firewall rules in place to prevent outbound connections on port 25, Hetzner by default will block this port until you’ve paid at least one month’s billing, and will only release the block if you formally request it. You’ll need to get the port unblocked before you can proceed - see below
https://docs.hetzner.com/cloud/servers/faq/#why-can-i-not-send-any-mails-from-my-server
Unfortunately, email spammers and scammers like to use cloud hosting providers. And we at Hetzner naturally want to prevent this. That’s why we block ports 25 and 465 by default on all cloud servers. This is a very common practice in the cloud hosting industry because it prevents abuse. We want to build trust with our new customers before we unblock these mail ports. Once you have been with us for a month and paid your first invoice, you can create a limit request to unblock these ports for a valid use case. In your request, you can tell us details about your use case. We make decisions on a case-by-case basis.
As an alternative, you can also use port 587 to send emails via external mail delivery services. Port 587 is not blocked and can be used without sending a limit request.
-
-
OUPS

Ok so I think it’s Hetzner who is blocking.
I will make them an unblocking request. -
-
Indeed. +1 for telnet.
I just trusted the netstats which told me that everything is OK which is certainly the case on the server.
since I didn’t have Telnet on hand I tested a website which told me OK

@DownPW said in Tutorial for secure emailing with personal domain,Cloudflare, virtualmin and postfix:
since I didn’t have Telnet on hand I tested a website which told me OK
I have to confess, I installed the
telnet-clienton your server for diagnostic purposes.Mark Cutting also advises organisations as a Fractional CIO, Fractional CISO and Executive Advisor, helping boards improve technology governance, cyber resilience and executive decision making. Learn more at Gratmore Ltd
-
OUPS
Ok so I think it’s Hetzner who is blocking.
I will make them an unblocking request.
@DownPW said in Tutorial for secure emailing with personal domain,Cloudflare, virtualmin and postfix:
I will make them an unblocking request.
Curious to know how you got on with this…
-

sorry for the late response my friends. They unblocked port 25 very quickly and I can send emails;
Just that the domains in caramail.com refused my sending of email for obscure reasons and protonmail, I receive them but in spam with an error message
I will share all its errors with you to see and I would like to deepen that the DMARC, and DKIM puts the private/public key which I do not really understand (see my request above)
PW and WS Spirit alive
-
sorry for the late response my friends. They unblocked port 25 very quickly and I can send emails;
Just that the domains in caramail.com refused my sending of email for obscure reasons and protonmail, I receive them but in spam with an error message
I will share all its errors with you to see and I would like to deepen that the DMARC, and DKIM puts the private/public key which I do not really understand (see my request above)
-
-
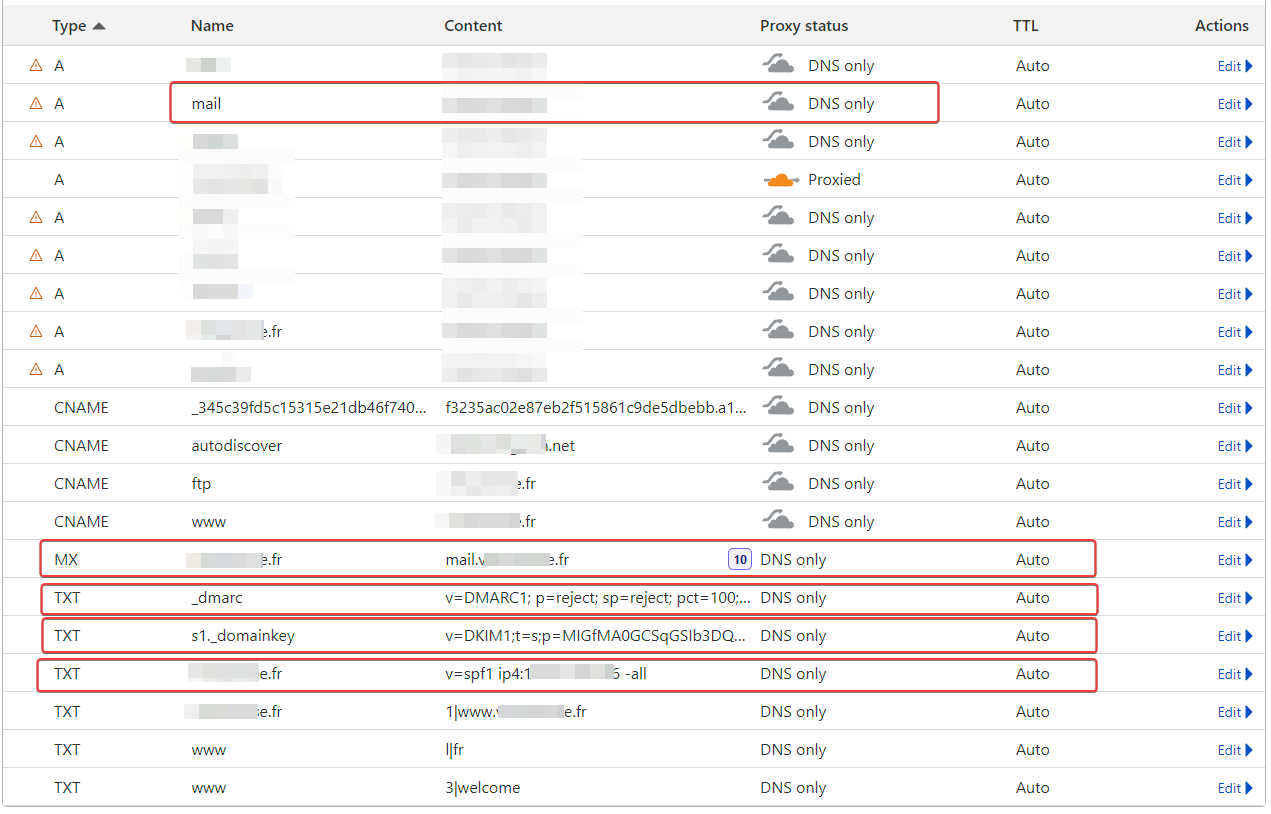
I have the DNS pointers present
-
-
Spf is on the screenshot
-
Spf is on the screenshot
-
-
Yep no problem
@DownPW thanks. See PM. You can validate your domain in terms of its email suitability by using the checker below
https://emailhealthcheckup.com/
In addition, there are some great generators and checkers here
-
Yep no problem

Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register LoginRelated Topics
-
-
-
-
-
-
-

Email issue (virturalmin)
Solved Hosting -