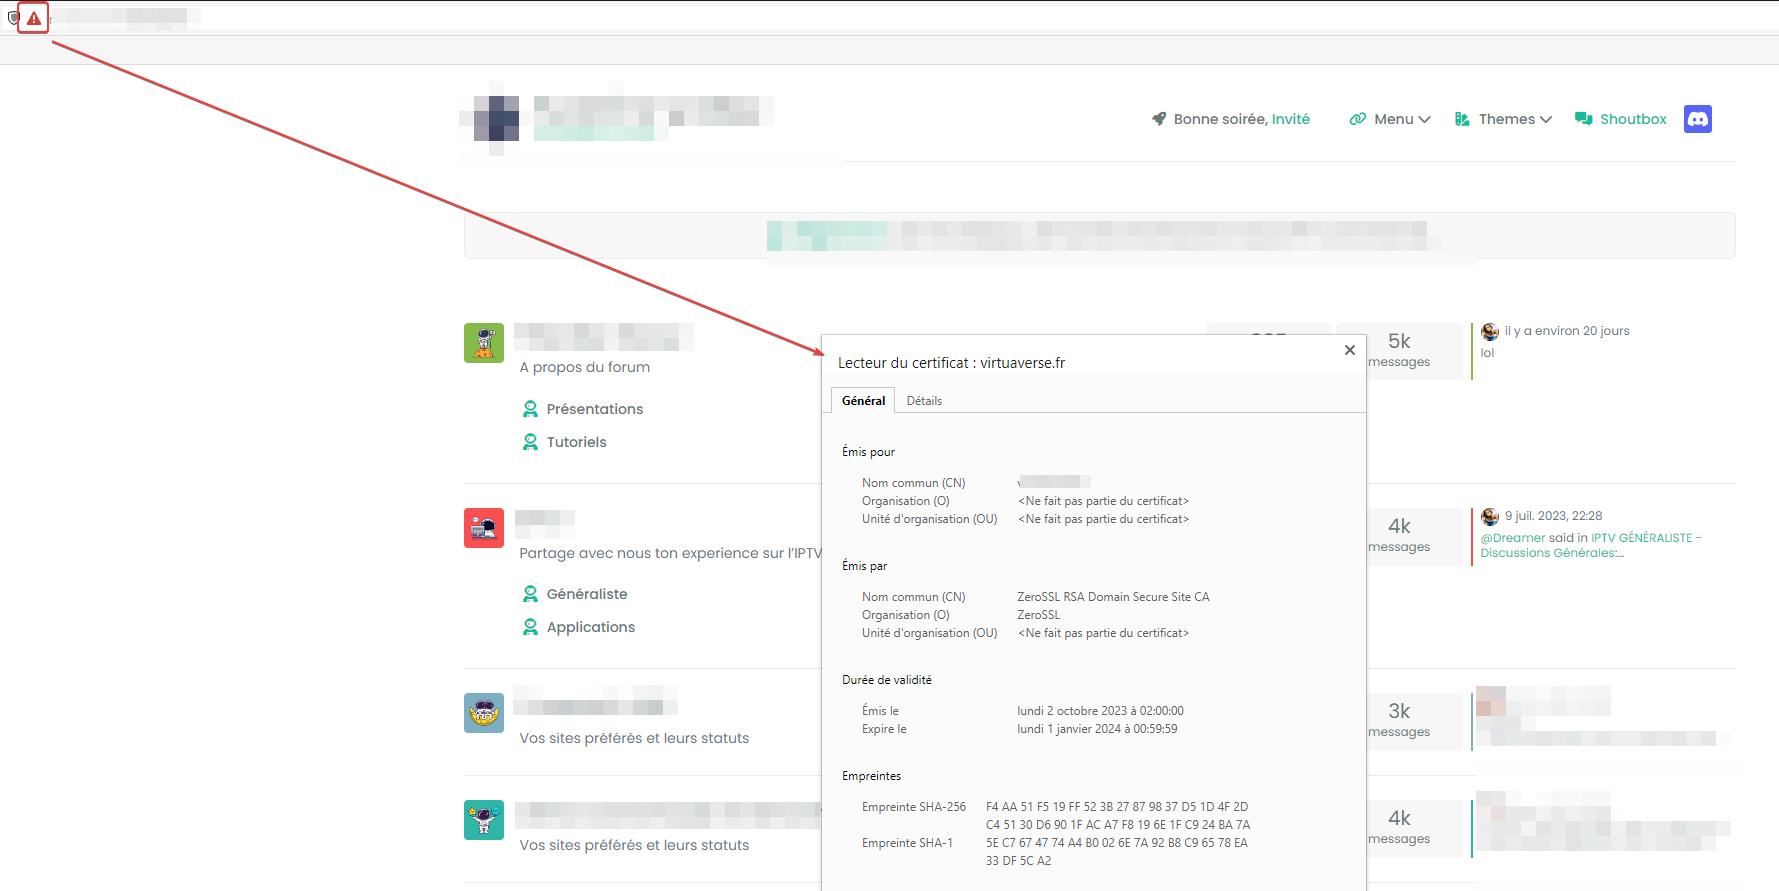
Digitalocean step by step guide to nginx configuration
-
@phenomlab ok, so i can add https, can i leave the ip or i need to add vfgest.it:3030?

@justoverclock You can use either, but if the API is not meant to be exposed publicly, and should only be accessed by the app itself, then you should use
127.0.0.1. Ultimately, the design is up to you.Mark Cutting also advises organisations as a Fractional CIO, Fractional CISO and Executive Advisor, helping boards improve technology governance, cyber resilience and executive decision making. Learn more at Gratmore Ltd
-
@justoverclock You can use either, but if the API is not meant to be exposed publicly, and should only be accessed by the app itself, then you should use
127.0.0.1. Ultimately, the design is up to you.
@phenomlab well, i’ve learned something new, no its a private crm developed by me, so no external use

-
@phenomlab well, i’ve learned something new, no its a private crm developed by me, so no external use
@justoverclock Exactly - that’s why I asked
You won’t be exposing the API then. Any issues, let me know.Mark Cutting also advises organisations as a Fractional CIO, Fractional CISO and Executive Advisor, helping boards improve technology governance, cyber resilience and executive decision making. Learn more at Gratmore Ltd
-
@justoverclock Exactly - that’s why I asked
You won’t be exposing the API then. Any issues, let me know.
@phenomlab ok i’ll try later when people are not using the crm :P, and i’ll post here the result

-
@phenomlab ok i’ll try later when people are not using the crm :P, and i’ll post here the result
@justoverclock No problems.
Mark Cutting also advises organisations as a Fractional CIO, Fractional CISO and Executive Advisor, helping boards improve technology governance, cyber resilience and executive decision making. Learn more at Gratmore Ltd
-
phenomlab has marked this topic as solved on
-
phenomlab referenced this topic on
-
@justoverclock No problems.
@phenomlab its odd but doesn’t work if i use https://vfgest.it:3030 or https://SERVERIP:3030 or https://127.0.0.1:3030
must be something related to proxy…because server and client are on the same server…but works if i restore all to previous unsecure http connection
-
@phenomlab its odd but doesn’t work if i use https://vfgest.it:3030 or https://SERVERIP:3030 or https://127.0.0.1:3030
must be something related to proxy…because server and client are on the same server…but works if i restore all to previous unsecure http connection
@justoverclock i’ve found an article that says
To resolve your issue you can setup nginx to proxy your http backend urls via https. With nginx server you will need to call your api like https://your_domain/api/some_path and nginx will proxy your request to api host, that you will set in configso my server actually is on port 3030, what should i do?
thx!
-
@justoverclock i’ve found an article that says
To resolve your issue you can setup nginx to proxy your http backend urls via https. With nginx server you will need to call your api like https://your_domain/api/some_path and nginx will proxy your request to api host, that you will set in configso my server actually is on port 3030, what should i do?
thx!
@justoverclock ok i’ve found the solution by myself watching your files…
-i’ve created a subdomain
- a new server blocks that proxy requests to the backend endpoint
- secured with certbot
all works fine

-
@justoverclock ok i’ve found the solution by myself watching your files…
-i’ve created a subdomain
- a new server blocks that proxy requests to the backend endpoint
- secured with certbot
all works fine
@justoverclock Beat me to it ! I was going to say that you could add another server block to the existing configuration, so for example
location /api {
                proxy_set_header X-Real-IP $remote_addr;
                proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
                proxy_set_header Host $http_host;
                proxy_set_header X-NginX-Proxy true;

                proxy_pass http://127.0.0.1:3030/;
                proxy_redirect off;

                # Socket.IO Support
                proxy_http_version 1.1;
                proxy_set_header Upgrade $http_upgrade;
                proxy_set_header Connection "upgrade";
}
Mark Cutting also advises organisations as a Fractional CIO, Fractional CISO and Executive Advisor, helping boards improve technology governance, cyber resilience and executive decision making. Learn more at Gratmore Ltd
-
@justoverclock Beat me to it ! I was going to say that you could add another server block to the existing configuration, so for example
location /api {
                proxy_set_header X-Real-IP $remote_addr;
                proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
                proxy_set_header Host $http_host;
                proxy_set_header X-NginX-Proxy true;

                proxy_pass http://127.0.0.1:3030/;
                proxy_redirect off;

                # Socket.IO Support
                proxy_http_version 1.1;
                proxy_set_header Upgrade $http_upgrade;
                proxy_set_header Connection "upgrade";
}
-
@phenomlab
 i’m learning ahahahah

@justoverclock said in Digitalocean step by step guide to nginx configuration:
i’m learning
And that’s the whole point of this site
If you don’t learn anything, you gain nothing.
Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register LoginDid this solution help you?
Related Topics
-
-
-
-
-
-
-
nginx can't start again
Moved Solved Configure -